Members
Invite your team, give each person a role, and suspend or remove people when they leave.
Where people live
Each member takes a paid seat, once per organization however many workspaces they're in. Pro and the free trial hold up to 5 members; Business and Enterprise have no cap. Guests review for free; see Guests.
- One workspace: SettingsMembers (Settings, then Members) lists everyone in the organization.
- Several workspaces: owners and admins manage everyone on the organization's Members page, under your organization's name in the settings sidebar. Each workspace's own Members and roles page lists the people in it, and its admins manage them there.
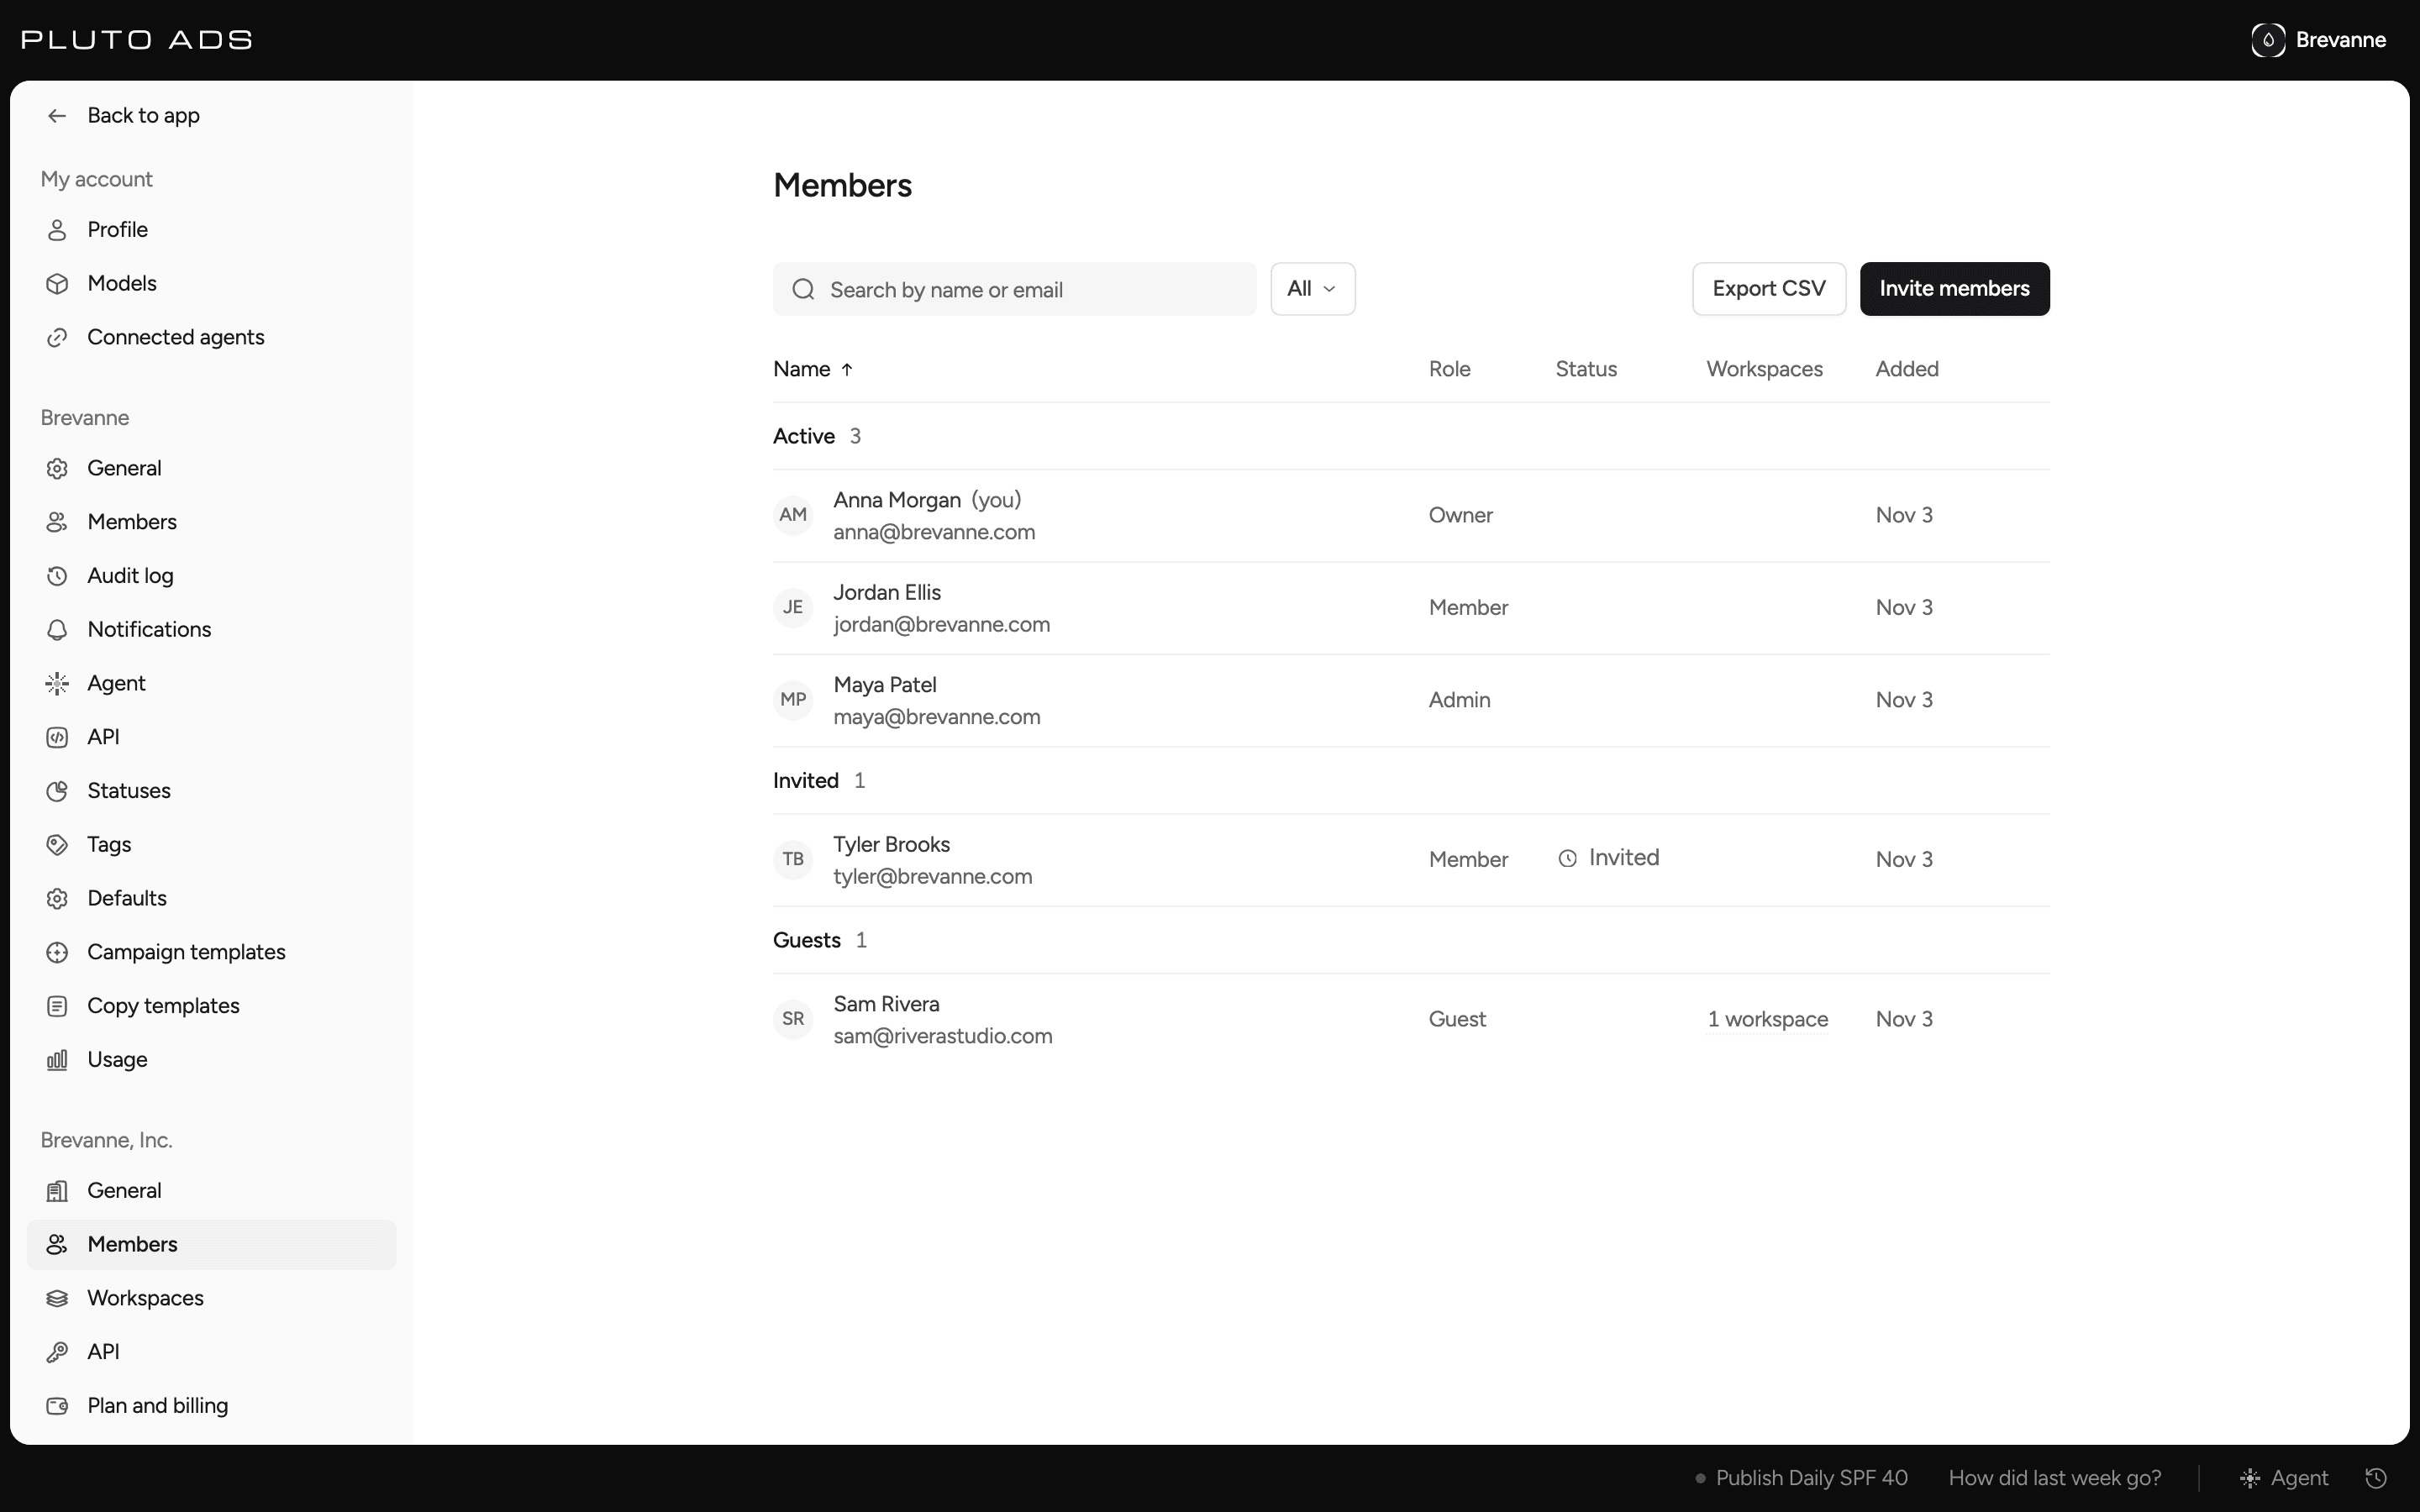
People are grouped as Active, Invited, Suspended and Guests. Search by name or email, filter by All, Members, Guests, Suspended or Invited, and download the list with Export CSV. A person's role is changed in the Role column; every other action is in the menu on their row.
Roles
Everyone has one role in each workspace they're in. Roles, beside Members on the same page, shows what each role allows: everything a role can do, in groups, with a check where a role has it.
| Role | What they can do |
|---|---|
| Owner | Everything, including ownership. |
| Admin | Everything but ownership: people, integrations, developer access and settings. |
| Manager | Builds, publishes and runs ads, live budgets and loops. No administration. |
| Media buyer | Builds and publishes ads, changes live budgets and pauses them. Doesn't delete at the platform. |
| Creative | Makes drafts and media, comments and approves. Nothing goes live. |
| Analyst | Views ads, results and spend, and saves views. |
| Guest | Comments on and approves the launches shared with guests. Free. |
The organization's owners and admins are owners and admins of every workspace. A member without a chosen role is a Manager.
Using the Agent and spending credits are part of a role:
- Use the Agent: every role but Guest. A role without it doesn't show the Agent anywhere: no bar at the bottom, no box on Home and no Agent settings of their own.
- Spend credits on Creative Memory analysis, Precision and competitor research: Owner, Admin, Manager, Media buyer and Creative. Without it, Add to Creative Memory isn't offered. Searching Creative Memory and reading what it found spends nothing, so everyone who views the workspace can, Analysts included.
To let a custom role use the Agent or spend credits, tick it on Roles. To cap what one person spends, set their credit limit.
To change someone's role, select it in the Role column and choose another. Each role says what it does. Roles you can't give are off, with the reason under the list: only owners make owners, only the organization's owners and admins turn a guest into a paid seat, and nobody gives a role that allows more than their own. Making a guest a member adds a seat, and the dialog shows what it adds to your bill. Only owners change an owner.
Nobody changes their own role, so your own row has no role to choose. An owner can step down once someone else is an owner (see Owners), and anyone can leave. API keys and agents can't change the role of the person they act for either.
With one workspace, SettingsMembers (Settings, then Members) offers that workspace's roles the same way, then Billing, under Organization, for someone who manages the plan, invoices and payment details, and your custom organization roles.
On a workspace's own Members and roles page, you can also make someone an admin of that workspace only: they manage it and invite its guests, but can't add paid seats.
What each line allows
Each line on Roles allows exactly what it says, and nothing beside it. What each one doesn't allow:
| Group | Allows | Doesn't allow |
|---|---|---|
| Ads and results | View ads, launches, analytics and spend | Doesn't change anything, and doesn't show lead form answers. |
| View lead form answers (personal data) | Doesn't create or change lead forms. | |
| Building | Create and edit launches and drafts | Doesn't publish or change anything live at the platform. |
| Upload and manage media | Doesn't add files to Creative Memory, which spends credits. | |
| Set up statuses, labels, country groups, copy templates and defaults | Doesn't change the workspace's settings or anyone's access. | |
| Save views and dashboards, and refresh results | Doesn't change ads, launches or anything at the platform. | |
| Collaboration | Comment, review and approve ads | Doesn't edit or publish the ads it approves. |
| Live ads | Publish and launch ads to the platform | Doesn't change live budgets, pause ads or delete them at the platform. |
| Change live budgets and bids | Doesn't publish new ads, pause them or delete them. | |
| Pause and resume live ads | Doesn't change budgets or publish edits. | |
| Delete ads at the platform | Doesn't publish, pause or change budgets. | |
| Reply to and hide comments on live ads | Doesn't change the ads the comments are on. | |
| Intelligence and automation | Spend credits on Creative Memory analysis, Precision and competitor research | Doesn't buy credits or raise anyone's limit. |
| Create and manage loops | Doesn't let a loop do more than whoever it acts as: each step needs its own capability. | |
| Use the Agent | Doesn't let the Agent do more than you may, and anything live waits for an approval. | |
| Administration | Invite people and change their roles | Doesn't give anyone more access than your own, make owners or add paid seats. |
| Connect platforms and integrations, and manage their ad accounts | Doesn't publish or change live ads, and an ad account's spending limit also needs changing live budgets. | |
| Export data | Doesn't export a whole workspace or everyone's usage, which need the organization's capabilities. | |
| View the audit log | Doesn't export the audit log, or show the organization's own, which is for its owners and admins. | |
| Change settings | Doesn't change who's in the workspace, its integrations or the organization's settings. | |
| Developer access | Create API keys | Doesn't give a key more access than your own, or touch other people's keys. |
| Connect agents to your account | Doesn't give an agent more access than your own, or connect one for anyone else. | |
| Register agent clients | Doesn't give an agent client more access than your own, or touch other people's clients. | |
| Manage webhooks | Doesn't create API keys or connect agents. | |
| Manage everyone's API keys and agents | Doesn't create keys or agents for other people, or give one more access than it has. | |
| Organization | Manage the organization's people | Doesn't grant or remove ownership, which only an owner does. |
| Create, archive and delete workspaces | Doesn't delete the organization, which only an owner does. | |
| Change organization settings and policies | Doesn't change billing, people or ownership. | |
| Billing | View billing | Doesn't change the plan, payment details, limits or credits. |
| Change billing and plan | Doesn't let an API key or agent complete a charge: a person signed in does. |
A loop's steps use only the first five groups: never administration, developer access, the organization or billing.
Custom roles
The organization's owners and admins make roles of their own on Roles. Select New role, choose the built-in role to start from, then name it, add one sentence on what it's for and tick what it allows. Ticking something ticks what it needs, such as viewing ads, and every custom role views the workspace. Through the API, a role without what one of its capabilities needs is refused, naming it. You can't give a role more than your own role allows. Custom roles take a paid seat, like members.
A custom role's menu, in its column, edits, duplicates or archives it. Everyone who holds a role gets a change at once. A role can be archived once nobody holds it.
Roles in a workspace never reach the organization's people, workspaces, settings or billing. For those, make an organization role: under New role, choose Admin or Billing under Organization role, then tick what it allows of the organization: invite and manage its people, create and archive workspaces, change its settings and policies, and view or change billing. Below the workspace's roles, Organization roles shows what each one allows, the built-in ones (Owner, Admin, Billing, Member, Guest) and yours, to the organization's owners and admins and anyone who manages its people. Give one in the Role column of the organization's Members page. Someone with an organization role still works in the workspaces they're given, with the role given there. As with every role, you can't give or make one that allows more than your own organization role.
Credit limit for one person
People who manage billing (the organization's owners and admins, and anyone with the Billing role) find Set credit limit... in the menu on a person's row. It opens Limits at that person, where you set how many credits they may use each month, or no limit. At their limit, what they spend credits on (the Agent, AI steps in loops and Creative Memory) pauses for them until the next period. See Billing.
Invite someone
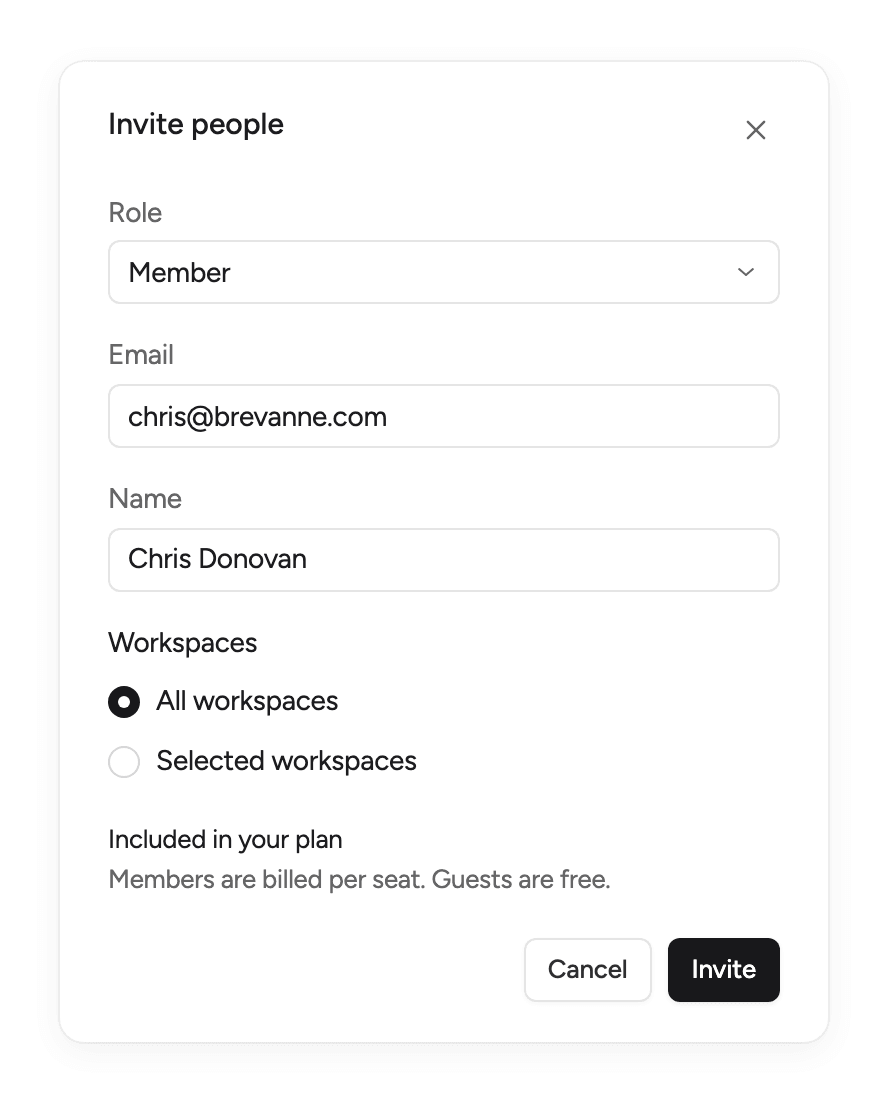
Before you send, the dialog shows whether a member adds a seat to your bill or is included in your plan. On Pro, a sixth member, counting pending invitations, needs Business: the dialog offers Upgrade to Business instead. We email them an Accept invitation link, and they accept by signing in with that address.
Invitations expire after 7 days. Resend invitation in the row menu sends a fresh one, and Revoke invitation cancels it. Resending is inviting again: you can resend only an invitation whose role you could give yourself. Only organization owners and admins add paid seats. A workspace's own admins can invite guests. A member invited from a workspace's own Members page joins the organization. On Pro and the trial they reach every workspace; on Business and Enterprise they can reach only that workspace.
An invitation is checked again when it's accepted, against the access of whoever sent it. If they can no longer give that role (they lost access, or the organization is down to one workspace, where an admin invitation makes an organization admin and needs an organization owner or admin), the invitation waits. The person invited is told it needs to be sent again by someone who can, and the audit log records it. Resend invitation from someone who can give the role lets them in when they next sign in.
Choose the workspaces a member reaches
Owners and admins reach every workspace. On Business and Enterprise, a member reaches all of them, new ones included, or only the ones you choose. On Pro and the trial, members reach every workspace. On the organization's Members page, choose Edit workspaces... in their row menu, pick all or selected, then Save access. The menu uses your organization's word, such as Edit clients... or Edit brands....
Suspend and reactivate
Suspend someone who shouldn't have access for now, for example during leave. Choose Suspend member... in their row menu. On the organization's page it suspends them everywhere; on a workspace's page, only in that workspace.
- Their access ends at once: sessions and live updates stop, also on their other devices.
- Their API keys, agent credentials, connected agents and Pluto MCP connections are revoked, and the webhooks they created, or that their keys and agents created, are turned off. The dialog lists them first.
- Loops that run as them pause, and admins are notified so someone can take them over.
- Suspended from the organization, they aren't billed as a seat.
- Their work stays, labeled with their name and (suspended).
Reactivate member... gives their access back, and they're billed as a seat again. Revoked API keys, agents and webhooks don't come back, and paused loops stay paused until someone turns them back on.
Only the organization's owners and admins suspend, reactivate or remove one of its owners or admins, also in a single workspace.
Remove someone
Choose Remove from organization... in their row menu. Removing does everything suspending does, ends their membership and frees their seat.
- Choose who takes over their loops and chats: an owner or admin. The loops stay paused until the new owner turns them back on.
- Choose what happens to their API keys and agent credentials. Revoke, the default, revokes them all. Hand over to me gives you each one you can hold: where you manage everyone's API keys and agents and your role covers its access. Each is re-issued to you with a new secret, and agent credentials of the Service type with a new client ID, and the old ones stop at once. The dialog lists what you'd take and, for each of the rest, why it's revoked instead. Their own agents, connected or acting for them, are never handed over.
- After you remove them, each new secret is shown once, one after another. Copy it before you select Done: it isn't shown again.
- Either way, their connected agents and Pluto MCP connections are revoked, and the webhooks they set up are turned off.
- Their comments and activity stay, labeled with their name and (former member).
Hand over to me isn't offered when you leave yourself, or when your organization turned it off in
Security. Through the API, removing someone takes the same choice (credentials), and
transfer_credentials still takes their keys over before they go.
On a workspace's Members page, Remove from workspace... ends their access to that workspace only. Their work there stays, and you choose the same for their API keys and agent credentials there.
Owners and admins leave an organization themselves: choose Leave organization... on your own row on the organization's Members page and pick the owner or admin who takes over your loops and chats. Members and guests don't have that page, so they ask an owner or admin to remove them.
Owners
An organization can have several owners. To make someone an owner, make them an admin first, then choose Owner in their Role column on the organization's Members page. Tick Step down to admin to step down yourself.
The last owner can't leave, be removed, be suspended or lose the owner role. Only an owner, signed in to Pluto Ads, can grant or remove ownership. No API key or agent can.
Audit log
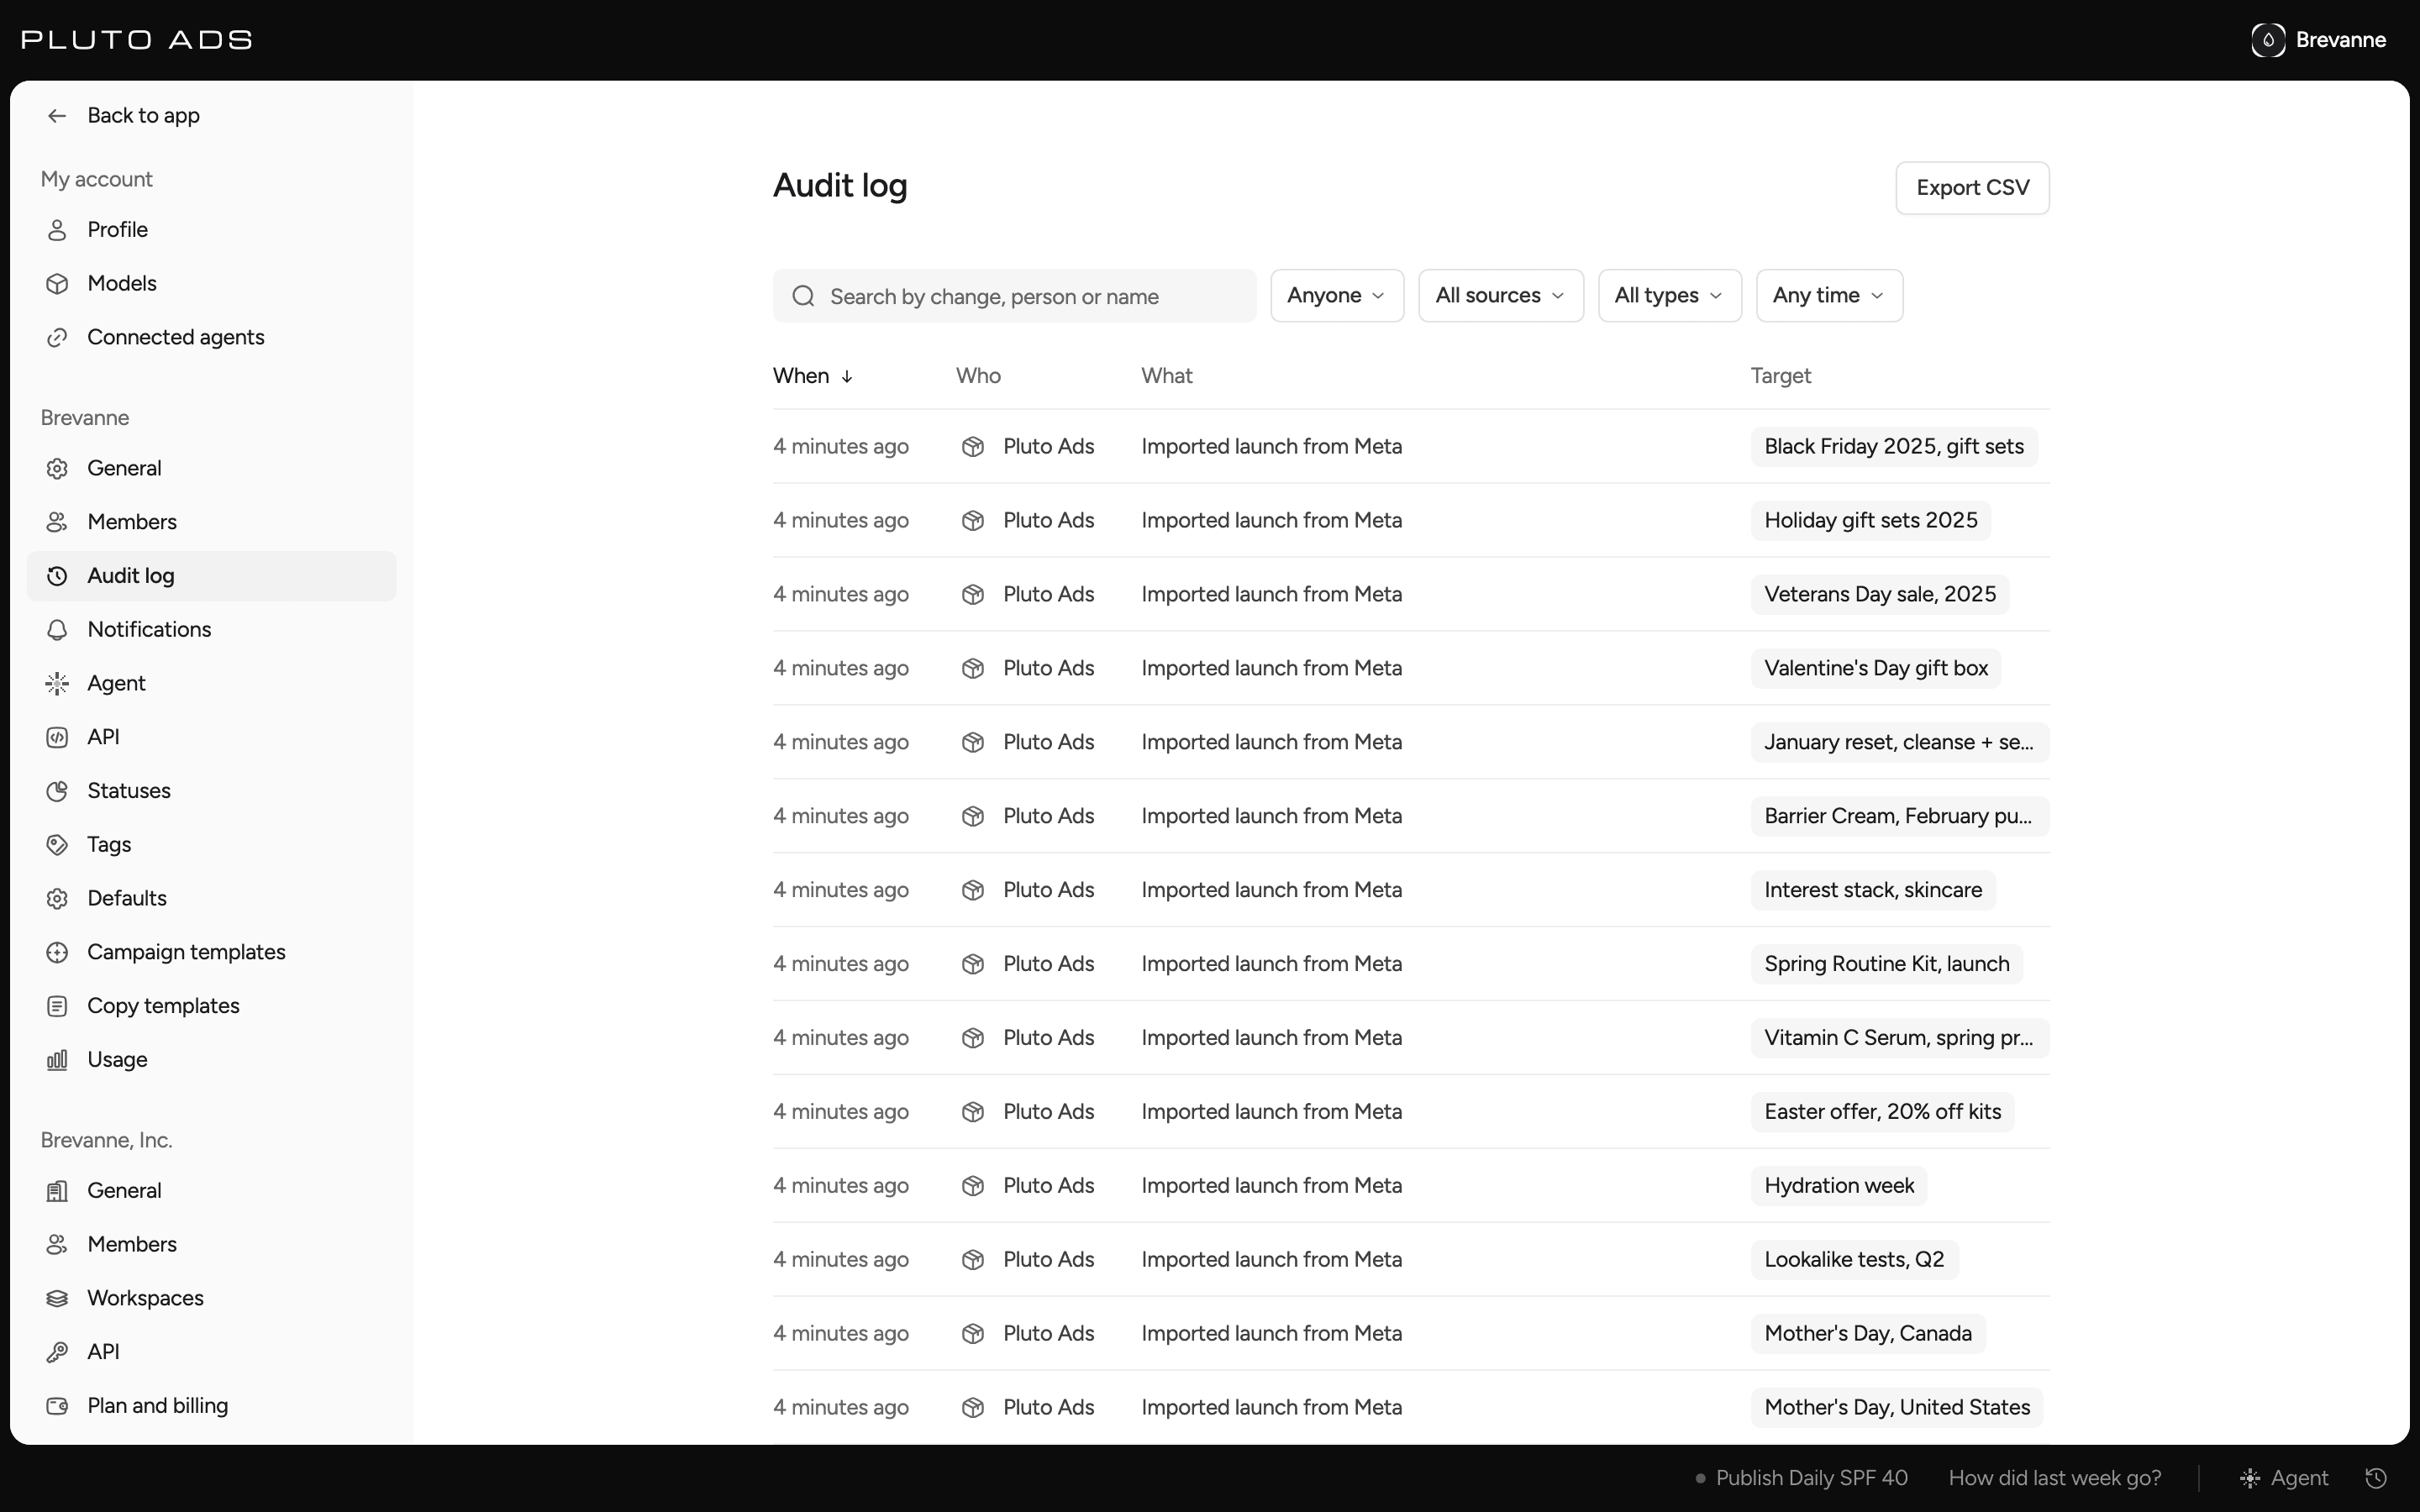
The audit log comes with Business and Enterprise. Admins of a workspace see SettingsAudit log (Settings, then Audit log): everything people, agents, loops and API keys changed in the workspace, with who did it, what changed, where it came from and the exact time. Where it matters, a line under the change says what it was before and after, such as a role going from Member to Admin, a member's status, a name, or what a role can now do and no longer do. Search it, and filter by person, source, kind and time.
Export CSV exports every change your filters match, however many there are:
- The file is made in the background. The button shows how far it got, like "Exporting... 420,000 of 1,200,000 rows", then turns into Download.
- You can leave the page. Your Inbox says when the file is ready. It's emailed to you too when you left the page before it was ready, or when it's large (it takes more than half a minute, or has more than 250,000 rows): then the page says so while it runs.
- The download link works for 7 days for anyone who can see the audit log. After that, export again.
- If an export doesn't finish, your Inbox says so. Nothing is emailed, and Export again starts it over.
- The file has one row per change, with the time in UTC, who did it and for whom, the API key or agent it came through, what it changed and the details. Its columns are listed in the Public API.
Changes to the whole organization are there too: its plan, billing details, credits and limits, members and invitations, who opened the billing portal or downloaded usage or workspace costs, the end of the free trial, and changes Stripe made to the subscription (a payment that failed, a subscription that ended). Only the organization's owners and admins see them, and someone who sees the audit log whose organization role includes managing the organization's people. With several workspaces, they're all on the organization's own Audit log, whichever workspace they were made from, with the same search, filters and export (see Organization). Each also appears in the workspace the change was made from, or in the organization's first workspace when it came from Pluto Ads. Complimentary access and Enterprise contracts that Pluto Ads sets up name the person at Pluto Ads who did it. When a change to the organization gives someone access to a workspace, changes their role there, suspends them or removes them, that workspace's own log shows it too, with the role before and after. An invitation that lapsed unused shows as expired, by Pluto Ads, with the address and role it was for; a revoked one shows them too. An API key, agent credentials or a connected agent that reached its expiry date shows as expired, by Pluto Ads, for the person it acted for.
Asking for the latest by hand is there too: syncing a platform, importing results now, reading a launch back from its platform, and checking whether Meta accepts changes again after you did what it asked. So is researching a competitor, with the files it gave Creative Memory and the most credits they use.
What someone's role, or a key's or agent's access, didn't let them do is there too: what it needed, what it was at and where it came from (the app, the API, an MCP client, the Agent, a loop, a plan, a background task, changes made offline, or connecting an integration). Trying the same thing again from the same place within a minute adds no new entry. Being refused something to view isn't listed.
Nobody can edit or delete an entry, Pluto Ads included. When a workspace is deleted, its entries stay and keep only IDs, numbers and fixed values such as roles; names, emails and text go. When someone deletes their account, the entries about them, their invitations and their API keys and agents are cut down the same way.
Good to know
- Seats, invitations, role changes and removals need a connection.
- While your organization is read-only, until it chooses a plan or fixes a payment, you can still remove people, leave and revoke invitations.
- Scripts and agents follow the same rules. See the Public API.