Organization
Your organization holds your workspaces, your people and your plan; its settings apply to every workspace in it.
Open the organization's settings
Signing up creates your organization with its first workspace. Only owners and admins change its settings. Its billing is also managed by anyone with the Billing role, who sees only the billing pages (see Who manages billing). The sidebar lists the pages your role reaches; a link to one it doesn't opens Home.
- With several workspaces, open Settings from the account menu (your workspace's name in the top bar). The settings sidebar has a block under the organization's name with General, Members, the workspaces page, API, Security, Audit log, Plan and billing, Usage and Limits. The Billing role finds Plan and billing, Usage and Limits there, and someone whose role manages everyone's API keys and agents in a workspace finds API.
- With one workspace, the organization's settings are on SettingsGeneral (Settings, then General), under the workspace's own, Security follows API in the sidebar, and Plan and billing, Usage and Limits sit under Billing.
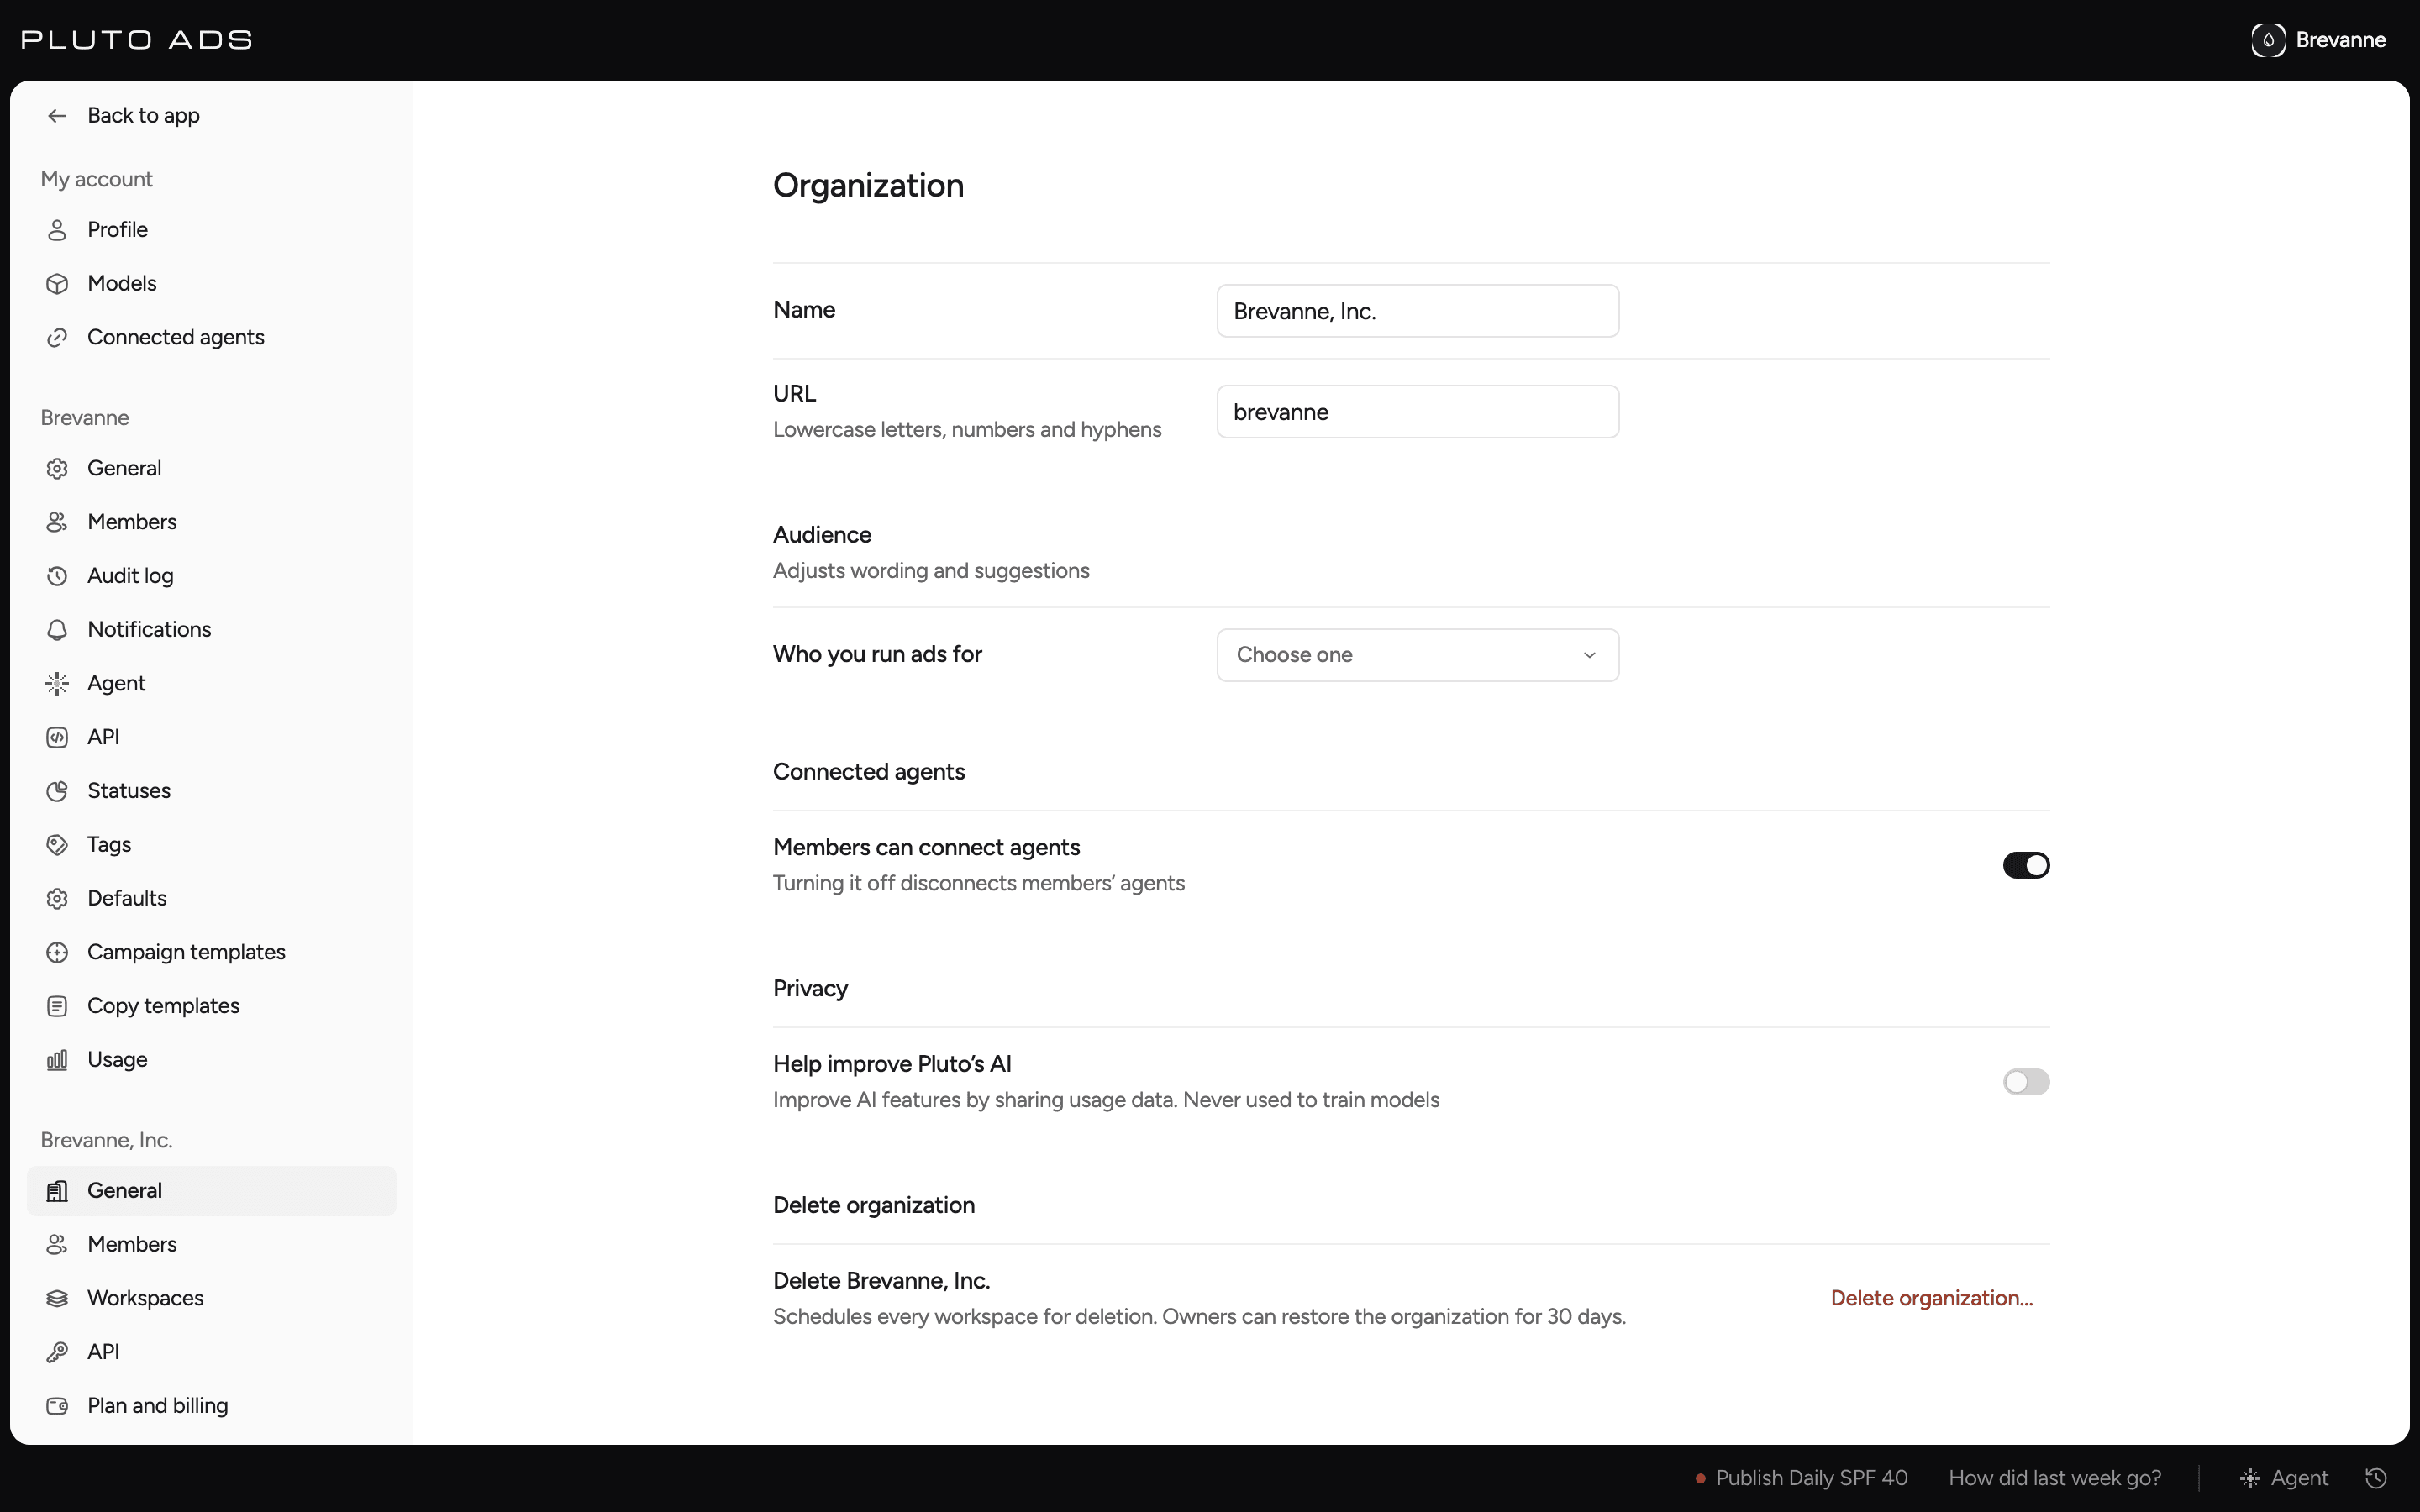
Name and URL name
The Organization page starts with the organization's Name and its URL name: 3 to 48 lowercase letters, numbers and hyphens. Select Save in the top bar to keep a change, or Discard to drop it.
Who you run ads for
Audience holds your answer to Who do you run ads for?, the question the Getting started checklist asks the organization's owner. Change it with Ads for:
| Choice | For | The app says |
|---|---|---|
| My brand | One brand or store | Workspace, where it needs a word at all |
| Several brands | A workspace for each brand | Brand, for example New brand |
| Clients | A workspace for each client | Client, for example New client |
It only changes words and suggestions, never how your organization works. Plans count clients for an agency and brands for everyone else.
Agents
Members can connect agents decides whether members may connect their own AI agents, such as Claude or Cursor. Owners and admins always can. Turning it off disconnects members' agents. See Connected agents.
Privacy
Help improve Pluto's AI shares usage data to improve AI features. It's never used to train models, and it's off until an owner or admin turns it on.
Security
Security holds what members may do with API keys, agents and webhooks, beyond their role. It binds everyone but the organization's owners and admins, including a workspace's admins who aren't the organization's. A choice saves as soon as you make it, and the audit log records each change with what it was before and after.
What members can create has a switch for API keys, Agent credentials and Webhooks. Turned off, only the organization's owners and admins create that kind: it's no longer in Add on SettingsAPI (Settings, then API) for anyone else, and the API refuses it. What members made before keeps working.
What members' keys and agents can do sets the most each kind may do, whatever the member's role allows:
- API keys, Agent credentials and Agents they connect: Everything their role allows, Build and publish or View results, the same choices as a key's Access. Under Build and publish they can view, build, upload media, review, publish and change live budgets and delivery, but not delete at the platform, reply to comments, see lead answers, use loops, credits or the Agent, or administer. New ones are offered only what fits. Ones made before are narrowed on their next request, never revoked: choosing more again gives back what they had.
- Longest a new credential lasts: No limit, 30 days, 90 days, 180 days, 365 days, or A number of days from 1 to 730, saved with Save in the top bar. API keys, agent credentials and agents members make then end within it, and Never isn't offered to them. Credentials made before keep the end they have.
When someone leaves has one switch, Hand over their keys. On, whoever removes someone can take over their API keys and agent credentials, each re-issued to them with a new secret (see Remove someone). Off, a leaving person's keys and agent credentials are always revoked, and nobody takes them over through the API either. Unlike the rest of Security, it applies to the organization's owners and admins too.
Members can connect agents, on General, still decides whether members connect agents at all, and turning it off stops the agents and agent credentials they have.
API
With several workspaces, the organization's API page lists its API keys and agents: every one for its owners and admins, and a workspace's for someone whose role manages everyone's API keys and agents there. Each is limited to its person's role, with what it can do, the person it acts for, who made it (like "API key 'Zapier' for Maya"), the addresses it works from, when it was last used and when it expires. The workspaces' webhooks are there too, each named by its endpoint, with the person it acts for, its last delivery and whether it delivers now (and if not, why), and so are the Pluto MCP connections people made. A webhook made by a key or agent with chosen ad accounts names them; one that sends every ad account's events doesn't say so. Filter the list by person, type and workspace, or show only what's Expiring within 7 days.
Whoever sees one acts on it from its menu, with one confirmation:
- Rotate key... replaces an API key with a new one that keeps its name, access and expiry. The new key is yours and shown once; the old one stops working at once, the keys and agent credentials it made are revoked with it, and the webhooks it made are turned off.
- Rotate secret... gives agent credentials a new secret, shown once, with the same client ID.
- Narrow access... gives an API key, agent credential or agent less access: it offers only what it can do now, and it keeps working with what you keep.
- Revoke access... stops an API key, agent, agent credential or Pluto MCP connection at once.
- Turn off... stops a webhook for good: no more events go to it.
A key or agent credential in an archived workspace can't be rotated, since the workspace is read-only; revoke it instead.
Through the API, they list, revoke and take over the same ones. With one workspace, SettingsAPI (Settings, then API) shows the same list. See the Public API.
Audit log
With several workspaces, the organization's Audit log lists what was done to the organization, from whichever of its workspaces: its plan, billing details, credits and limits, members, invitations and roles. Only the organization's owners and admins see it, and someone who sees a workspace's audit log whose organization role includes managing the organization's people, on Business and Enterprise. It reads like a workspace's audit log: who did it (a person, or an agent, loop or API key and the person it acted for), what changed, with the value before and after where it matters, such as a role or a status, where it came from and the exact time. Search it, filter it by person, source, type and time, and export it as CSV. With one workspace, these changes are in that workspace's SettingsAudit log (Settings, then Audit log). See Members.
Belong to several organizations
One account can belong to several organizations, for example your own brand and a client's. Choose Switch organization in the account menu to move between them. Your profile is the same in each; see Your account.
Delete an organization
Only an owner, signed in to Pluto Ads, can delete an organization.
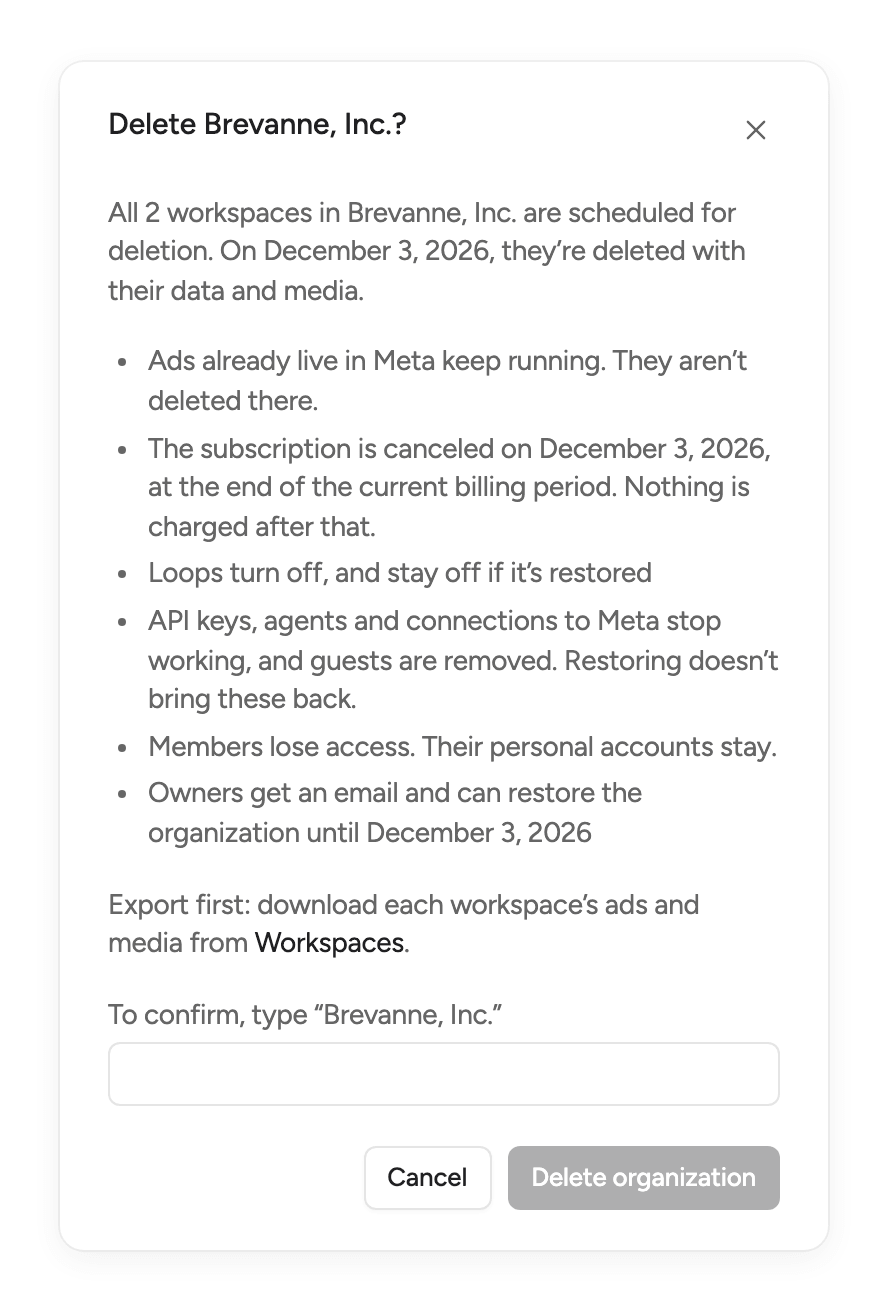
When you delete an organization:
- Every workspace in it is scheduled for deletion, with its data and media, 30 days from now.
- Ads already live in Meta keep running. Nothing is deleted in Meta.
- The subscription is canceled at the end of the current billing period. Nothing is charged after that.
- Loops pause.
- API keys, agents and the connections to Meta stop working, and guests are removed.
- X is disconnected in every workspace, and live ads keep running. What Pluto Ads read from X is deleted right away, as X's terms ask.
- Members lose access. Their personal accounts stay, with their other organizations.
- Owners get an email, and can restore the organization until the date.
Export what you want to keep first: each workspace's menu on the organization's workspaces page has an export. See Workspaces.
Restore an organization
Until the date, an owner can restore it from the link in the email, or by signing in and selecting Restore organization. Workspaces come back as they were, and an archived one comes back archived.
What doesn't come back by itself:
- Loops stay paused until someone turns them back on.
- Create new API keys, invite guests again, and reconnect Meta.
- If the billing period ended, subscribe again in Plan and billing.
Members who aren't owners see the deletion date and can ask an owner to restore it. After the date, the organization, its workspaces, their data and media are deleted for good.
Good to know
- Settings on this page need a connection.
- No API key or agent can delete or restore an organization.
- A workspace deleted on its own before keeps its own deletion date.